Recomendations
 |
Strategy and Management
Include security in business plans and KPIs
Source: it.portal
|
More information, which may be usefull to you, may be found after login at it-portal.sk
|
 Actual incidents
|
6 |
What is what in IT
|
66 |
je pokus o podvodné získanie citlivých informácií, ako sú heslá, údaje o kreditných kartách, vydávaním sa za dôveryhodnú osobu alebo inštitúciu pri elektronickej komuniká... more...
means the possible time of use of the service, hardware, software or other resources for operation, given in %.
show all
Interesting
|
22 |
Source: CheckPoint Research
Tens of thousands of Microsoft Exchange email servers in Europe, the US and Asia are vulnerable to remote code execution. There is a version of the software in the mail s... more...
show all
Recomendations
|
377 |
Your computer, smartphone, Wi-Fi router and all IT devices must always have the latest versions of operating system updates and patches installed. This also applies t... more...
Source: KCCKB
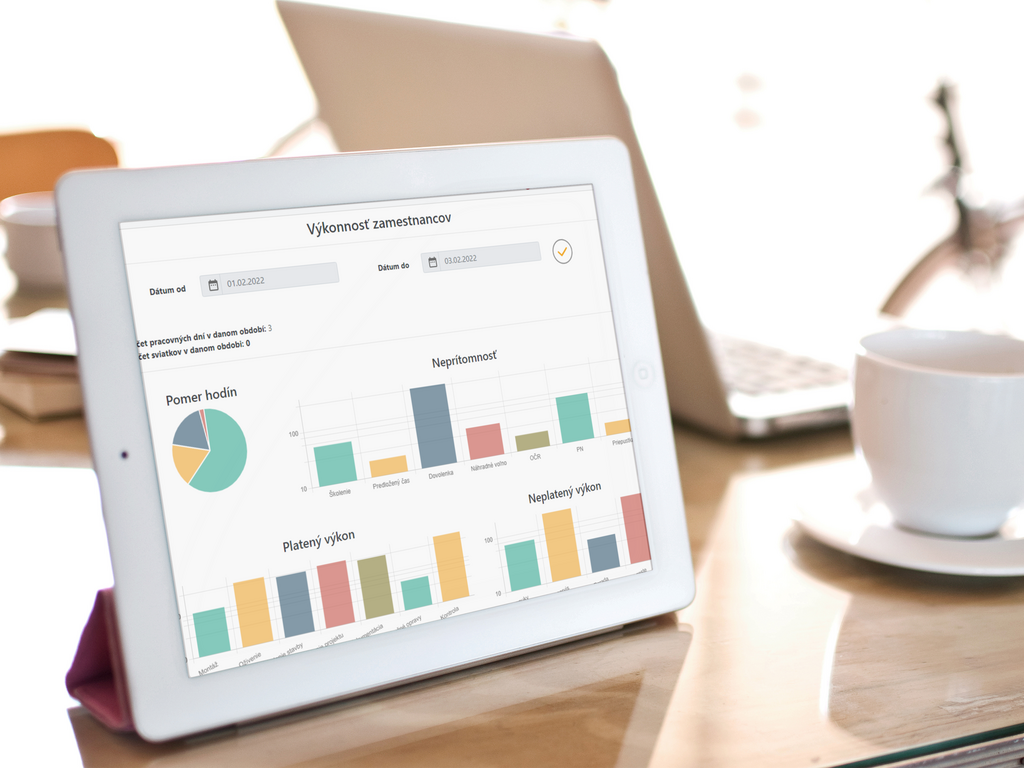
Implement reporting and dashboard for management
Source: it.portal
show all
Institutions
|
51 |
Eyvor, National Coordination Centre for Cybersecurity - The Electronic Communications Office of Iceland (ECOI) show link
National Cybersecurity Institute (INCIBE) show link
show all
Legislative
|
82 |
Zákon o kritickej infraštruktúre a o zmene a doplnení niektorých zákonov show link
Source: Slov-Lex
Vyhláška Národného bezpečnostného úradu o personálnej bezpečnosti show link
Source: Slov-Lex
show all
Norms
|
25 |
Information technology — Security techniques — Code of practice for information security controls based on ISO/IEC 27002 for cloud services
Source: ISO
Information technology — Security techniques — Code of practice for protection of personally identifiable information (PII) in public clouds acting as PII processors
more...
Source: ISO
show all
Technologies
|
14 |
Infographics
|
7 |
To ale neznamená, že sú jediné
Source: Google Maps
show all
Events
|
0 |
Certifications
|
0 |
Acreditations
|
0 |
Media
|
436 |
|

 SK
 CZ
 EN